Cyber Security Mississauga: Build Skills for a Safer Digital Future
Digital technology has changed the way businesses communicate, store information, serve customers, and manage daily operations. While these changes create new opportunities, they also introduce security risks that organizations cannot afford to ignore. Data breaches, phishing attacks, malware, account compromises, and network vulnerabilities can affect organizations of almost every size.
For students and professionals interested in cyber security Mississauga, this growing focus on digital protection creates opportunities to develop practical technical skills and prepare for security-focused careers. Understanding how networks, systems, applications, and users can be protected is becoming increasingly valuable in a technology-driven workplace.
Why Cybersecurity Matters Today
Modern organizations depend on connected systems. Employees access cloud platforms, communicate through email, work remotely, store customer information, and use multiple applications throughout the day. Each connection can become a potential security risk when it is not properly protected.
Cybersecurity focuses on reducing those risks through a combination of technology, processes, monitoring, and user awareness. Security professionals may help organizations detect suspicious activity, control access to systems, protect sensitive information, investigate incidents, and strengthen security practices.
Interest in Mississauga cybersecurity continues to be relevant because the city is home to businesses across industries such as technology, transportation, finance, healthcare, manufacturing, logistics, and professional services. Organizations operating in digitally connected environments need people who understand how to recognize and respond to technology-related risks.
Cybersecurity is not simply about stopping hackers. It involves understanding how systems operate, identifying weak points, managing access, monitoring activity, and responding appropriately when something unusual happens.
What Does a Cybersecurity Analyst Do?
A cybersecurity analyst helps protect an organization's technology infrastructure and information from potential threats.
The exact responsibilities vary depending on the organization, but analysts may work with security monitoring tools, network systems, firewalls, user accounts, endpoint protection platforms, security policies, and incident response procedures.
Common responsibilities can include:
- Reviewing security alerts and system activity
- Identifying unusual login attempts or network behaviour
- Investigating possible security incidents
- Checking systems for vulnerabilities
- Supporting access control and authentication processes
- Reviewing security configurations
- Documenting incidents and findings
- Helping employees understand security practices
- Assisting with security assessments
- Supporting recovery after cybersecurity incidents
Strong analysts combine technical knowledge with critical thinking. Finding a security alert is only the first step. A professional must determine what happened, understand the level of risk, document the issue clearly, and help decide what action should follow.
Learning the Skills Needed for Cybersecurity
A well-designed cybersecurity analyst program can introduce learners to the technical and analytical skills commonly associated with entry-level security roles. Rather than focusing only on theory, cybersecurity education is most useful when learners can practise troubleshooting, monitoring, investigation, and security configuration.
Students should build a strong understanding of computer networking. Concepts such as IP addresses, ports, protocols, routers, switches, DNS, firewalls, and network traffic provide the foundation for understanding how attacks and security controls work.
Operating systems are equally important. Cybersecurity professionals frequently interact with Windows and Linux environments, making command-line familiarity and system administration knowledge valuable.
Important Technical Areas to Study
Someone considering a cyber security analyst course should look beyond the course title and examine the actual topics covered. Effective cybersecurity training should provide a balanced understanding of networking, operating systems, security fundamentals, threat detection, access management, and incident response.
Several technical areas are particularly useful for beginners.
Network Security
Network security teaches learners how data moves between systems and how organizations protect their networks from unauthorized access.
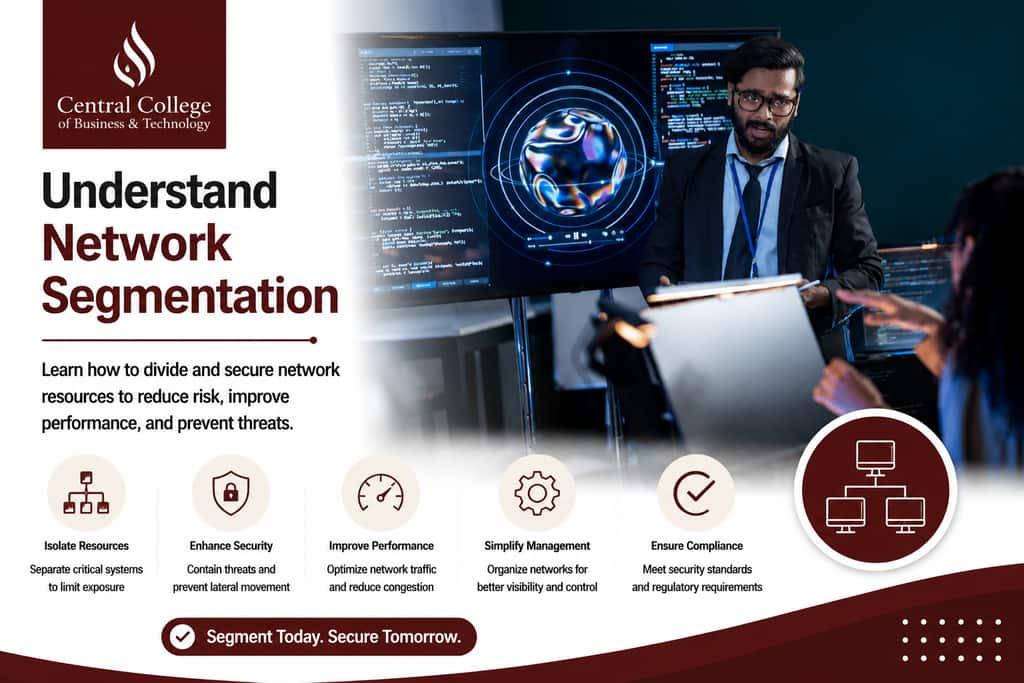
Students may learn about firewalls, virtual private networks, network segmentation, common protocols, monitoring, and suspicious traffic patterns.
Understanding normal network behaviour makes it easier to recognize activity that may indicate a security problem.
Threats and Vulnerabilities
Cybersecurity students should understand common attack methods and system weaknesses.
Examples can include phishing, malware, password attacks, social engineering, insecure configurations, outdated software, and unauthorized access attempts.
The goal is not simply to memorize different attacks. Students should understand how vulnerabilities are discovered, why they create risks, and what defensive controls can reduce exposure.
Identity and Access Management
Organizations must control who can access information, systems, and applications.
Learning concepts such as authentication, authorization, multi-factor authentication, least privilege, user permissions, and account management helps students understand how identity-based security works.
Poor access management can create significant security problems even when other security tools are correctly configured.
Security Monitoring
Security teams often monitor systems for unusual activity.
Students may benefit from learning how logs are generated, collected, reviewed, and interpreted. Understanding security alerts can help future analysts determine whether unusual activity represents a genuine threat or normal system behaviour.
Good analysts learn to investigate before making assumptions.
Incident Response
Even organizations with strong security controls can experience security incidents.
Incident response focuses on identifying what happened, containing the problem, reducing further damage, recovering affected systems, and documenting lessons learned.
A structured response helps security teams avoid confusion during high-pressure situations.
Practical Skills Matter as Much as Theory
Reading about cybersecurity provides useful knowledge, but practical exercises help turn concepts into skills.
Learners should look for opportunities to practise with virtual machines, operating systems, network configurations, log files, security monitoring environments, and controlled cybersecurity labs.
For example, a student may examine login logs and identify repeated failed authentication attempts. Another exercise might involve finding an insecure system configuration and recommending a safer setup.
These practical scenarios help students understand how security concepts apply in real environments.
Develop Strong Problem-Solving Skills
Cybersecurity professionals regularly work with incomplete information.
An alert may indicate unusual activity without clearly explaining what caused it. Analysts must investigate different possibilities, examine evidence, compare events, and decide what deserves further attention.
A useful problem-solving process is:
- Identify the unusual activity.
- Gather relevant information.
- Check logs and supporting evidence.
- Determine which systems or accounts are affected.
- Assess the potential security impact.
- Recommend an appropriate response.
- Document the investigation.
Following a structured process can reduce mistakes and improve the quality of security investigations.
Do Not Ignore Communication Skills
Technical ability is important, but cybersecurity professionals also need strong communication skills.
Analysts may need to explain technical risks to managers, employees, clients, or other IT professionals who have different levels of technical knowledge.
Clear documentation is particularly important. Incident reports should explain what happened, what systems were affected, what actions were taken, and what should happen next.
Professionals who can translate complex technical information into simple language often work more effectively across teams.
Build a Strong Cybersecurity Foundation
Beginners sometimes try to learn advanced security tools before understanding basic IT concepts. Building foundational knowledge first usually creates a stronger learning path.
Start with networking, operating systems, computer hardware, cloud concepts, user permissions, and basic system administration.
Then move toward security monitoring, vulnerabilities, risk management, incident response, penetration testing concepts, and security automation.
Learning basic scripting can also be valuable. Languages such as Python can help security professionals automate repetitive tasks, process information, and analyze system data.
Create Your Own Practice Environment
A personal cybersecurity lab can help learners practise without affecting production systems.
Virtualization software can be used to create isolated Windows and Linux systems where students can explore operating systems, network configurations, permissions, logging, and defensive security tools.
Always practise cybersecurity techniques only on systems you own or have explicit permission to test.
Ethical behaviour is an essential part of professional cybersecurity.
Keep Learning as Technology Changes
Cybersecurity requires continuous learning because technology changes constantly.
New cloud services, applications, operating systems, security tools, attack techniques, and defensive methods appear regularly. Professionals should continue improving their skills through documentation, technical labs, industry publications, security communities, and structured training.
Instead of trying to learn everything at once, focus on developing strong fundamentals and gradually expanding into more specialized areas.
Possible future areas of specialization include cloud security, security operations, digital forensics, vulnerability management, identity security, application security, governance and risk, and incident response.
Conclusion
Cybersecurity offers a technical career path for people who enjoy problem-solving, investigation, technology, and continuous learning. Success begins with understanding computer systems and networks before progressing into threat detection, security monitoring, access management, vulnerability analysis, and incident response.
Building practical experience is just as important as learning terminology. Working with labs, reviewing logs, troubleshooting systems, and practising structured investigations can help transform theoretical knowledge into useful professional skills.
For learners in Mississauga, developing strong cybersecurity foundations can prepare them to better understand modern digital risks and pursue opportunities in an increasingly security-conscious technology environment.

 English
 Arabic
 French
 Spanish
 Portuguese
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)
 Greek
 ไทย